The evidence is mixed or incomplete, so the website deserves a careful manual check. A fully valid TLS certificate was not confirmed. The accessible homepage exposed a contact route and linked policy or company information. Confidence is high based on 7 distinct evidence groups collected during the latest scan. The result is a risk assessment, not proof that vipzd.co is legitimate or fraudulent.
Is vipzd.co safe?
Independent website safety report covering the connection, domain history, browser protections, page behavior and reputation signals observed by DarkOra.
What the latest scan says about vipzd.co
DarkOra separates technical evidence from community opinion and explains the factors behind the score.
TLS validation unavailable
Registration provider unavailable
0 of 6 monitored headers
MDN HTTP Observatory result
Evidence that influenced the score
Review both columns. A high total score does not cancel a material caution signal.
Signals that support trust
Website responded successfully
The scanned destination returned HTTP 200.
HTTP · transport · +3 pointsContact route found
The page exposes a contact or support page, a visible email address.
Content · transparency · +2 pointsNormal homepage content was accessible
The scanner received a usable HTML homepage rather than an interstitial or access-control page.
Content · behavior · +2 pointsNo monitored high-risk wording detected
The accessible homepage did not contain the monitored high-pressure or credential-request phrases.
Content · behavior · +2 pointsResponsive origin server
The initial request completed in about 9 ms.
Performance · transport · +1 pointsPublic DNS resolution
The domain resolves to 1 validated public network address.
DNS · domain · +1 pointsPublic routing identity found
RIPEstat mapped the address to AS141718 and prefix 43.250.125.0/24.
RIPEstat · domain · +1 pointsDescriptive page title
The homepage provides a usable browser title.
Content · transparency · +1 pointsPage description is provided
The homepage includes a descriptive meta summary.
Content · transparency · +1 pointsSome policy information is linked
At least one policy or company-information page was found.
Content · transparency · +1 pointsSubstantive homepage content
The scanned page contains enough readable text to explain its purpose.
Content · transparency · +1 pointsNo hidden frames or external form targets
The accessible homepage did not expose hidden iframes or forms posting to another hostname.
Content · behavior · +1 pointsSignals worth reviewing
HTTPS is not enforced
The final page is delivered over unencrypted HTTP.
Transport · transport · -8 pointsTLS service unavailable
A valid certificate could not be collected from the standard HTTPS port.
TLS · transport · -6 pointsWeak MDN Observatory grade
MDN HTTP Observatory assigned grade F, indicating weak browser hardening.
MDN HTTP Observatory · security · -2 pointsLimited nameserver redundancy
Fewer than two authoritative nameservers were detected.
DNS · domain · -1 pointsRegistration age unavailable
Public RDAP data did not provide a reliable registration date.
RDAP · domain · -1 pointsMissing strict-transport-security
The response did not include this browser security header. Missing headers affect hardening, but do not by themselves prove fraud.
Security headers · security · -1 pointsMissing content-security-policy
The response did not include this browser security header. Missing headers affect hardening, but do not by themselves prove fraud.
Security headers · security · -1 pointsFraming protection not found
No X-Frame-Options or CSP frame-ancestors rule was detected.
Security headers · security · -1 pointsMissing x-content-type-options
The response did not include this browser security header. Missing headers affect hardening, but do not by themselves prove fraud.
Security headers · securityMissing referrer-policy
The response did not include this browser security header. Missing headers affect hardening, but do not by themselves prove fraud.
Security headers · securityMissing permissions-policy
The response did not include this browser security header. Missing headers affect hardening, but do not by themselves prove fraud.
Security headers · securityNetwork, certificate and page-level observations
These values were captured at scan time and may change after a server, DNS or certificate update.
Infrastructure footprint
- Resolved IP addresses
- 43.250.125.104
- Authoritative nameservers
- 0
- Mail / MX records
- 0
- CAA policy
- Not found
- SPF policy
- Not found
- DMARC policy
- Not found
Connection security
- HTTP status
- 200
- Final protocol
- HTTP
- Certificate validation
- Not validated
- Certificate issuer
- Unavailable
- TLS protocol / cipher
- Unavailable
- Certificate expires
- Unavailable
Registration context
- Approximate age
- Unavailable
- Registered
- Unavailable
- Expires
- Unavailable
- Registrar
- Unavailable
- RDAP status entries
- 0
- RDAP available
- No
0/6 monitored protections detected
External security and reputation context
Provider failures stay separate from the base scan. DarkOra never fabricates a provider result.
DNSSEC authenticated data
The provider answered, but authenticated DNSSEC data was not confirmed.
Response code 0 · 2 answersIndependent header grade
MDN evaluated the live HTTP security configuration independently from DarkOra.
10 points · 7/12 tests passedPreload-list status
The hostname is not currently confirmed as preloaded. This alone is not a scam indicator.
Independent transport-hardening contextRouting and origin identity
The scanned address maps to prefix 43.250.125.0/24.
BGP present · registry presentOfficial threat-list context
The optional official Web Risk integration is not configured.
Checked Nov 3, 2026Official profile lookup
Trustpilot requires an official API key. DarkOra does not scrape profile pages.
Open Trustpilot profileResponse and redirect details
- Origin address used
- 43.250.125.104
- Server header
- PROXY-V8-PRO
- Content type
- text/html
- Downloaded response
- 20,557 bytes
- Redirect hops
- 0
- Initial response time
- 9 ms
What the homepage exposes
- Internal links
- 22
- External links
- 5
- External-link ratio
- 19%
- Forms detected
- 0
- Suspicious phrase groups
- 0
- Scanner methodology
- Version 4.0.0
Questions about this website safety report
Plain-language answers explain what the score can and cannot tell you.
Is vipzd.co safe to visit?+
The evidence is mixed or incomplete, so the website deserves a careful manual check. A fully valid TLS certificate was not confirmed. The accessible homepage exposed a contact route and linked policy or company information. Confidence is high based on 7 distinct evidence groups collected during the latest scan. The result is a risk assessment, not proof that vipzd.co is legitimate or fraudulent.
What is the DarkOra score for vipzd.co?+
The latest DarkOra website safety score is 48 out of 100, classified as Caution advised. The score reflects observable technical and reputation evidence collected during the latest scan.
How is this website safety score calculated?+
DarkOra uses six independently capped areas: connection and TLS, domain maturity and DNS, browser security, identity and transparency, page behavior, and external reputation. No single signal determines the entire score.
When was vipzd.co last checked?+
The report was last updated on November 3, 2026. Website, DNS and certificate settings can change after this time.
Does a high score prove that vipzd.co is legitimate?+
No. Automated evidence can reduce uncertainty, but it cannot prove ownership, product quality or honest intent. Verify the organization, payment destination, refund terms and independent reputation before sharing sensitive information.
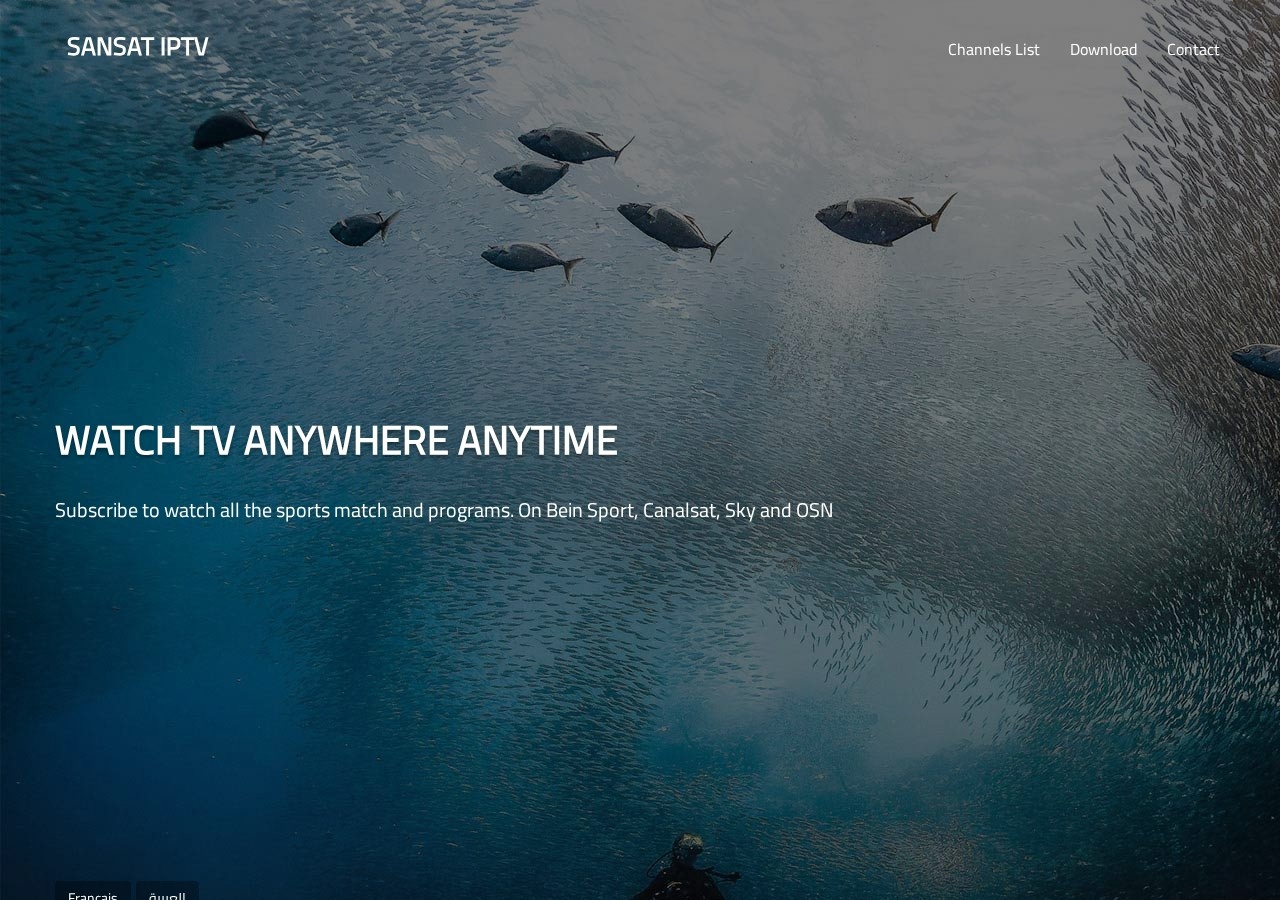
Reviews from DarkOra members
Account-linked reviews are screened for spam and published only after manual moderation.
No approved community review yet
Be the first member to describe a direct experience with this website.
Write a review
Sign in with your DarkOra account to submit a moderated review.
Sign in to reviewUse this report as one part of your decision. Automated checks can miss newly created threats and may flag legitimate configurations. Verify the organization, payment recipient, refund terms and independent reputation before sharing money, credentials or sensitive data.
