Website security intelligenceHigh confidence

Is sp7.szczecin.pl safe?

Independent website safety report covering the connection, domain history, browser protections, page behavior and reputation signals observed by DarkOra.

https://sp7.szczecin.pl/ HTTP 200
Last analyzedOctober 21, 2026
Evidence collected24 signals
Scan duration10,949 ms
REPORT OVERVIEW

What the latest scan says about sp7.szczecin.pl

DarkOra separates technical evidence from community opinion and explains the factors behind the score.

Assessment summary

The available evidence contains more reassuring signals than material concerns. Its TLS certificate was valid at scan time. Registration records show the domain has existed for more than two years. The accessible homepage exposed a contact route and no obvious policy links. Confidence is high based on 7 distinct evidence groups collected during the latest scan. The result is a risk assessment, not proof that sp7.szczecin.pl is legitimate or fraudulent.

18Positive factors
6Caution factors
24Total signals
ConnectionHTTPS

Valid TLS certificate observed

Domain history20.1 years

nazwa.pl sp. z o.o.

Browser hardening17%

1 of 6 monitored headers

Independent gradeC-

MDN HTTP Observatory result

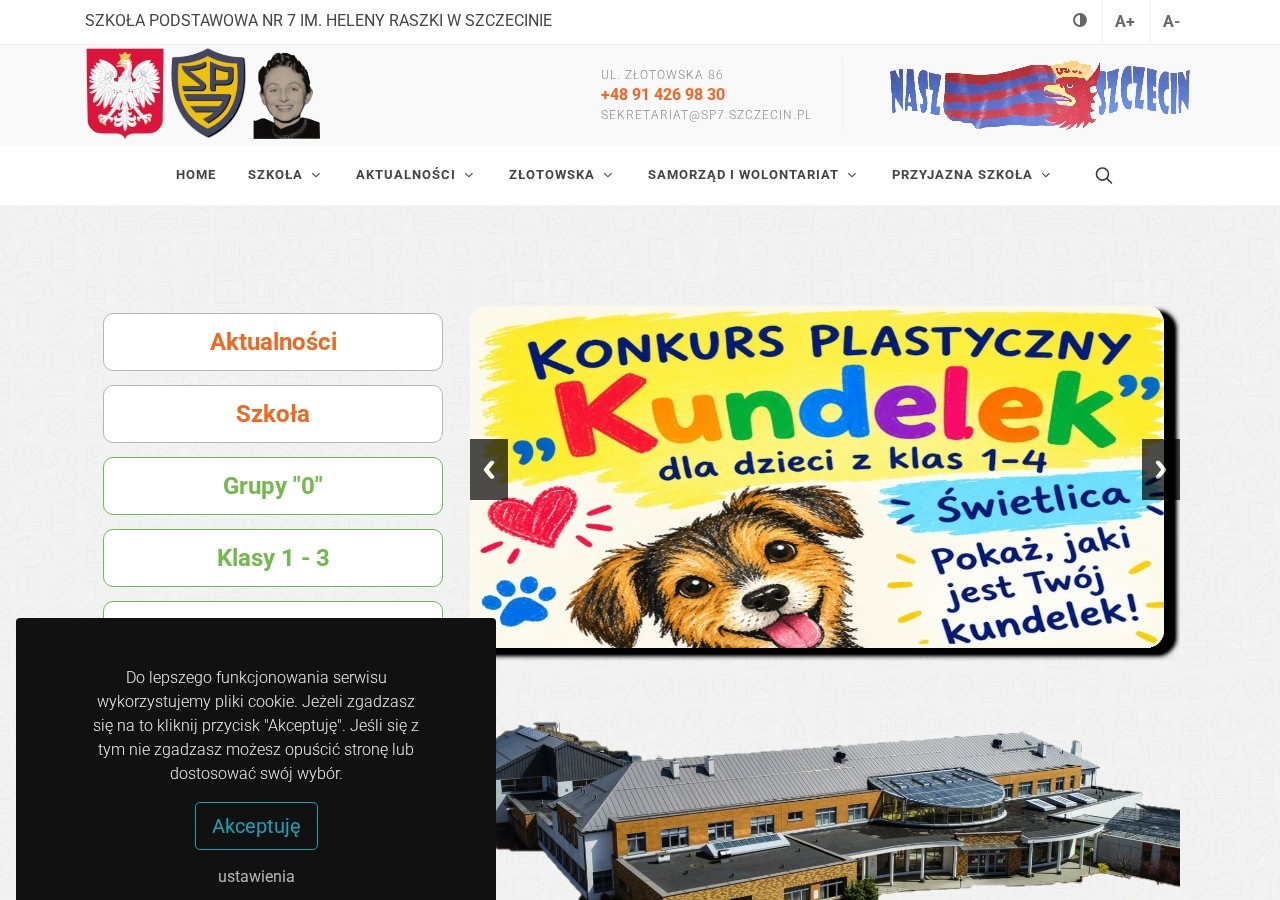
CAPTURED HOMEPAGE

Visual snapshot from the scan

https://sp7.szczecin.pl/
Screenshot of sp7.szczecin.pl captured during the latest DarkOra website safety scan
KEY FINDINGS

Evidence that influenced the score

Review both columns. A high total score does not cancel a material caution signal.

POSITIVE FACTORS

Signals that support trust

18

Valid TLS certificate

The certificate is trusted, matches the hostname and is currently valid.

TLS · transport · +7 points

HTTPS is active

The final page is delivered through an encrypted HTTPS connection.

Transport · transport · +4 points

Long-established domain registration

Registration records indicate an age of about 20 years.

RDAP · domain · +4 points

Website responded successfully

The scanned destination returned HTTP 200.

HTTP · transport · +3 points

Domain email controls are published

The domain exposes multiple mail-routing or anti-spoofing controls.

DNS · domain · +2 points

Contact route found

The page exposes a visible email address.

Content · transparency · +2 points

Normal homepage content was accessible

The scanner received a usable HTML homepage rather than an interstitial or access-control page.

Content · behavior · +2 points

No monitored high-risk wording detected

The accessible homepage did not contain the monitored high-pressure or credential-request phrases.

Content · behavior · +2 points

Responsive origin server

The initial request completed in about 1489 ms.

Performance · transport · +1 points

Public DNS resolution

The domain resolves to 1 validated public network address.

DNS · domain · +1 points

Nameserver redundancy

At least two authoritative nameservers were found.

DNS · domain · +1 points

Public routing identity found

RIPEstat mapped the address to AS12824 and prefix 89.161.128.0/18.

RIPEstat · domain · +1 points

Clickjacking protection

Framing is restricted through X-Frame-Options or CSP.

Security headers · security · +1 points

Descriptive page title

The homepage provides a usable browser title.

Content · transparency · +1 points

robots.txt is available

The website publishes a non-empty robots.txt file.

Public files · transparency · +1 points

Substantive homepage content

The scanned page contains enough readable text to explain its purpose.

Content · transparency · +1 points

No hidden frames or external form targets

The accessible homepage did not expose hidden iframes or forms posting to another hostname.

Content · behavior · +1 points

Canonical URL declared

The page declares a canonical destination.

Content · transparency
CAUTION FACTORS

Signals worth reviewing

6

Policy links not found

Privacy, terms, refund or company-information links were not detected.

Content · transparency · -2 points

Missing strict-transport-security

The response did not include this browser security header. Missing headers affect hardening, but do not by themselves prove fraud.

Security headers · security · -1 points

Missing content-security-policy

The response did not include this browser security header. Missing headers affect hardening, but do not by themselves prove fraud.

Security headers · security · -1 points

Missing x-content-type-options

The response did not include this browser security header. Missing headers affect hardening, but do not by themselves prove fraud.

Security headers · security

Missing referrer-policy

The response did not include this browser security header. Missing headers affect hardening, but do not by themselves prove fraud.

Security headers · security

Missing permissions-policy

The response did not include this browser security header. Missing headers affect hardening, but do not by themselves prove fraud.

Security headers · security
TECHNICAL EVIDENCE

Network, certificate and page-level observations

These values were captured at scan time and may change after a server, DNS or certificate update.

NETWORK & DNS

Infrastructure footprint

Resolved IP addresses
89.161.174.143
Authoritative nameservers
3
Mail / MX records
1
CAA policy
Not found
SPF policy
Published
DMARC policy
Published
HTTPS & TLS

Connection security

HTTP status
200
Final protocol
HTTPS
Certificate validation
Trusted and valid
Certificate issuer
TLS protocol / cipher
TLSv1.3 TLS_AES_256_GCM_SHA384
Certificate expires
November 30, 2026
DOMAIN RECORD

Registration context

Approximate age
20.1 years
Registered
September 8, 2006
Expires
September 8, 2027
Registrar
nazwa.pl sp. z o.o.
RDAP status entries
0
RDAP available
Yes
BROWSER SECURITY HEADERS

1/6 monitored protections detected

17%
HSTSNot detected
Content Security PolicyNot detected
X-Frame-OptionsSAMEORIGIN
X-Content-Type-OptionsNot detected
Referrer-PolicyNot detected
Permissions-PolicyNot detected
INDEPENDENT SIGNALS

External security and reputation context

Provider failures stay separate from the base scan. DarkOra never fabricates a provider result.

GOOGLE PUBLIC DNSNot validated

DNSSEC authenticated data

The provider answered, but authenticated DNSSEC data was not confirmed.

Response code 0 · 1 answers
MDN HTTP OBSERVATORYC-

Independent header grade

MDN evaluated the live HTTP security configuration independently from DarkOra.

45 points · 8/12 tests passed
CHROMIUM HSTS PRELOADUnknown

Preload-list status

The hostname is not currently confirmed as preloaded. This alone is not a scam indicator.

Independent transport-hardening context
RIPESTAT NETWORKAS12824

Routing and origin identity

The scanned address maps to prefix 89.161.128.0/18.

BGP present · registry present
GOOGLE WEB RISK—

Official threat-list context

The optional official Web Risk integration is not configured.

Checked Oct 21, 2026
TRUSTPILOT—

Official profile lookup

Trustpilot requires an official API key. DarkOra does not scrape profile pages.

Open Trustpilot profile
HTTP DELIVERY

Response and redirect details

Origin address used
89.161.174.143
Server header
IdeaWebServer/6.4.2
Content type
text/html; charset=UTF-8
Downloaded response
52,357 bytes
Redirect hops
0
Initial response time
1,489 ms
CONTENT FOOTPRINT

What the homepage exposes

Internal links
153
External links
4
External-link ratio
3%
Forms detected
2
Suspicious phrase groups
0
Scanner methodology
Version 4.0.0
REPORT GUIDANCE

Questions about this website safety report

Plain-language answers explain what the score can and cannot tell you.

Is sp7.szczecin.pl safe to visit?+

The available evidence contains more reassuring signals than material concerns. Its TLS certificate was valid at scan time. Registration records show the domain has existed for more than two years. The accessible homepage exposed a contact route and no obvious policy links. Confidence is high based on 7 distinct evidence groups collected during the latest scan. The result is a risk assessment, not proof that sp7.szczecin.pl is legitimate or fraudulent.

What is the DarkOra score for sp7.szczecin.pl?+

The latest DarkOra website safety score is 77 out of 100, classified as Low observed risk. The score reflects observable technical and reputation evidence collected during the latest scan.

How is this website safety score calculated?+

DarkOra uses six independently capped areas: connection and TLS, domain maturity and DNS, browser security, identity and transparency, page behavior, and external reputation. No single signal determines the entire score.

When was sp7.szczecin.pl last checked?+

The report was last updated on October 21, 2026. Website, DNS and certificate settings can change after this time.

Does a high score prove that sp7.szczecin.pl is legitimate?+

No. Automated evidence can reduce uncertainty, but it cannot prove ownership, product quality or honest intent. Verify the organization, payment destination, refund terms and independent reputation before sharing sensitive information.
COMMUNITY EXPERIENCE

Reviews from DarkOra members

Account-linked reviews are screened for spam and published only after manual moderation.

No approved community review yet

Be the first member to describe a direct experience with this website.

SHARE A DIRECT EXPERIENCE

Write a review

Use this report as one part of your decision. Automated checks can miss newly created threats and may flag legitimate configurations. Verify the organization, payment recipient, refund terms and independent reputation before sharing money, credentials or sensitive data.