Website security intelligenceHigh confidence

Is facebook.com safe?

Independent website safety report covering the connection, domain history, browser protections, page behavior and reputation signals observed by DarkOra.

https://www.facebook.com/ HTTP 200
Last analyzedSeptember 21, 2026
Evidence collected28 signals
Scan duration8,011 ms
REPORT OVERVIEW

What the latest scan says about facebook.com

DarkOra separates technical evidence from community opinion and explains the factors behind the score.

Assessment summary

The available evidence contains more reassuring signals than material concerns. Its TLS certificate was valid at scan time. Registration records show the domain has existed for more than two years. The accessible homepage exposed no clear contact route and no obvious policy links. Confidence is high based on 7 distinct evidence groups collected during the latest scan. The result is a risk assessment, not proof that facebook.com is legitimate or fraudulent.

23Positive factors
5Caution factors
28Total signals
ConnectionHTTPS

Valid TLS certificate observed

Domain history29.5 years

RegistrarSafe, LLC

Browser hardening83%

5 of 6 monitored headers

Independent grade

MDN HTTP Observatory result

CAPTURED HOMEPAGE

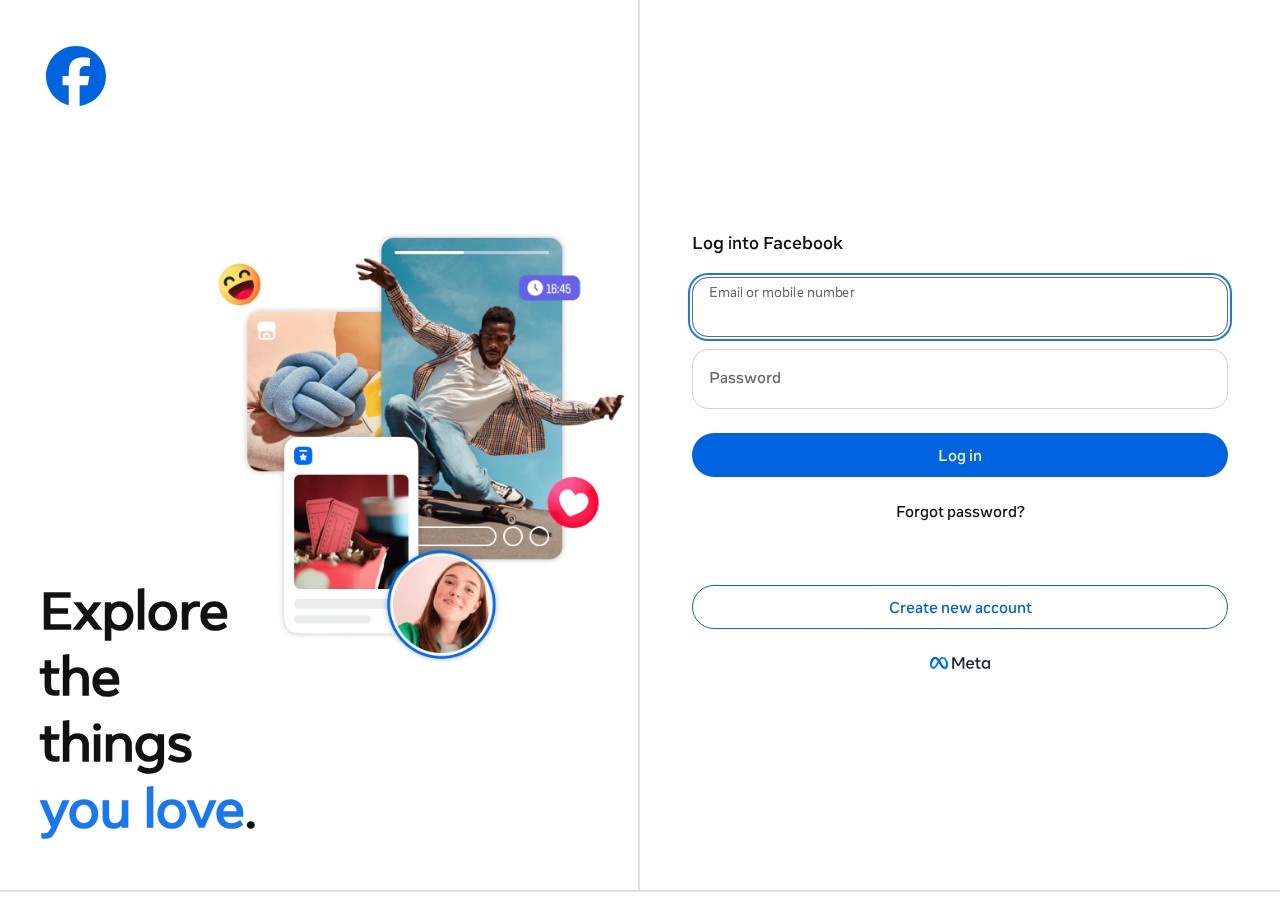
Visual snapshot from the scan

https://www.facebook.com/
Screenshot of facebook.com captured during the latest DarkOra website safety scan
KEY FINDINGS

Evidence that influenced the score

Review both columns. A high total score does not cancel a material caution signal.

POSITIVE FACTORS

Signals that support trust

23

Valid TLS certificate

The certificate is trusted, matches the hostname and is currently valid.

TLS · transport · +7 points

HTTPS is active

The final page is delivered through an encrypted HTTPS connection.

Transport · transport · +4 points

Long-established domain registration

Registration records indicate an age of about 29 years.

RDAP · domain · +4 points

Website responded successfully

The scanned destination returned HTTP 200.

HTTP · transport · +3 points

Domain email controls are published

The domain exposes multiple mail-routing or anti-spoofing controls.

DNS · domain · +2 points

HSTS is present

The response includes the strict-transport-security header.

Security headers · security · +2 points

Content Security Policy is present

The response includes the content-security-policy header.

Security headers · security · +2 points

security.txt is available

A security contact file was found under .well-known.

Public files · transparency · +2 points

Normal homepage content was accessible

The scanner received a usable HTML homepage rather than an interstitial or access-control page.

Content · behavior · +2 points

No monitored high-risk wording detected

The accessible homepage did not contain the monitored high-pressure or credential-request phrases.

Content · behavior · +2 points

Public DNS resolution

The domain resolves to 2 validated public network addresses.

DNS · domain · +1 points

Nameserver redundancy

At least two authoritative nameservers were found.

DNS · domain · +1 points

Certificate authority policy

CAA records restrict which authorities may issue certificates.

DNS · domain · +1 points

Public routing identity found

RIPEstat mapped the address to AS32934 and prefix 57.144.220.0/23.

RIPEstat · domain · +1 points

MIME sniffing protection is present

The response includes the x-content-type-options header.

Security headers · security · +1 points

Permissions policy is present

The response includes the permissions-policy header.

Security headers · security · +1 points

Clickjacking protection

Framing is restricted through X-Frame-Options or CSP.

Security headers · security · +1 points

HSTS preload list entry

The hostname is included in Chromium’s HSTS preload status data.

Chromium HSTS Preload · security · +1 points

Descriptive page title

The homepage provides a usable browser title.

Content · transparency · +1 points

robots.txt is available

The website publishes a non-empty robots.txt file.

Public files · transparency · +1 points

Consistent canonical redirect

Redirects remain within the same domain family.

HTTP · behavior · +1 points

No hidden frames or external form targets

The accessible homepage did not expose hidden iframes or forms posting to another hostname.

Content · behavior · +1 points

Canonical URL declared

The page declares a canonical destination.

Content · transparency
CAUTION FACTORS

Signals worth reviewing

5

Certificate expires soon

The current certificate has 14 days or less remaining.

TLS · transport · -2 points

Policy links not found

Privacy, terms, refund or company-information links were not detected.

Content · transparency · -2 points

Contact route not found

No clear email, telephone or support route was detected on the homepage.

Content · transparency · -1 points

Very limited page content

The homepage contains little readable text.

Content · transparency · -1 points

Missing referrer-policy

The response did not include this browser security header. Missing headers affect hardening, but do not by themselves prove fraud.

Security headers · security
TECHNICAL EVIDENCE

Network, certificate and page-level observations

These values were captured at scan time and may change after a server, DNS or certificate update.

NETWORK & DNS

Infrastructure footprint

Resolved IP addresses
57.144.220.1, 2a03:2880:f36e:1:face:b00c::25de
Authoritative nameservers
4
Mail / MX records
1
CAA policy
Published
SPF policy
Published
DMARC policy
Published
HTTPS & TLS

Connection security

HTTP status
200
Final protocol
HTTPS
Certificate validation
Trusted and valid
Certificate issuer
TLS protocol / cipher
TLSv1.3 TLS_CHACHA20_POLY1305_SHA256
Certificate expires
September 28, 2026
DOMAIN RECORD

Registration context

Approximate age
29.5 years
Registered
March 29, 1997
Expires
March 30, 2034
Registrar
RegistrarSafe, LLC
RDAP status entries
6
RDAP available
Yes
BROWSER SECURITY HEADERS

5/6 monitored protections detected

83%
HSTSmax-age=15552000; preload
Content Security Policydefault-src blob: 'self' https://*.fbsbx.com *.facebook.com *.fbcdn.net *.whatsapp.com *.whatsapp.n…
X-Frame-OptionsDENY
X-Content-Type-Optionsnosniff
Referrer-PolicyNot detected
Permissions-Policyaccelerometer=(), attribution-reporting=(self), autoplay=(), bluetooth=(), browsing-topics=(self),…
INDEPENDENT SIGNALS

External security and reputation context

Provider failures stay separate from the base scan. DarkOra never fabricates a provider result.

GOOGLE PUBLIC DNSNot validated

DNSSEC authenticated data

The provider answered, but authenticated DNSSEC data was not confirmed.

Response code 0 · 1 answers
MDN HTTP OBSERVATORY

Independent header grade

No completed Observatory result was available during this run.

No score · 0/0 tests passed
CHROMIUM HSTS PRELOADPreloaded

Preload-list status

Browsers can enforce HTTPS before the first network request.

Independent transport-hardening context
RIPESTAT NETWORKAS32934

Routing and origin identity

The scanned address maps to prefix 57.144.220.0/23.

BGP present · registry present
GOOGLE WEB RISK

Official threat-list context

The optional official Web Risk integration is not configured.

Checked Sep 21, 2026
TRUSTPILOT

Official profile lookup

Trustpilot requires an official API key. DarkOra does not scrape profile pages.

Open Trustpilot profile
HTTP DELIVERY

Response and redirect details

Origin address used
57.144.220.1
Server header
Content type
text/html; charset="utf-8"
Downloaded response
410,427 bytes
Redirect hops
1
Initial response time
3,181 ms
CONTENT FOOTPRINT

What the homepage exposes

Internal links
0
External links
0
External-link ratio
0%
Forms detected
0
Suspicious phrase groups
0
Scanner methodology
Version 4.0.0
REPORT GUIDANCE

Questions about this website safety report

Plain-language answers explain what the score can and cannot tell you.

Is facebook.com safe to visit?+

The available evidence contains more reassuring signals than material concerns. Its TLS certificate was valid at scan time. Registration records show the domain has existed for more than two years. The accessible homepage exposed no clear contact route and no obvious policy links. Confidence is high based on 7 distinct evidence groups collected during the latest scan. The result is a risk assessment, not proof that facebook.com is legitimate or fraudulent.

What is the DarkOra score for facebook.com?+

The latest DarkOra website safety score is 79 out of 100, classified as Low observed risk. The score reflects observable technical and reputation evidence collected during the latest scan.

How is this website safety score calculated?+

DarkOra uses six independently capped areas: connection and TLS, domain maturity and DNS, browser security, identity and transparency, page behavior, and external reputation. No single signal determines the entire score.

When was facebook.com last checked?+

The report was last updated on September 21, 2026. Website, DNS and certificate settings can change after this time.

Does a high score prove that facebook.com is legitimate?+

No. Automated evidence can reduce uncertainty, but it cannot prove ownership, product quality or honest intent. Verify the organization, payment destination, refund terms and independent reputation before sharing sensitive information.
COMMUNITY EXPERIENCE

Reviews from DarkOra members

Account-linked reviews are screened for spam and published only after manual moderation.

No approved community review yet

Be the first member to describe a direct experience with this website.

SHARE A DIRECT EXPERIENCE

Write a review

Use this report as one part of your decision. Automated checks can miss newly created threats and may flag legitimate configurations. Verify the organization, payment recipient, refund terms and independent reputation before sharing money, credentials or sensitive data.