Skip to content
DarkOraFree Website Safety Checker
Strong trust signalsNovember 16, 2026

Is invader.shop safe?

Website safety & security report · High confidence

Website Safety Score

DARKORA INDEX

Threat listsNot checked

SSL / TLSValid certificate

Security headers5 / 6 detected

RESOLVED IP188.114.96.0
HTTP FETCH TIME365 ms
SERVER HEADERcloudflare
DOMAIN AGE4.6 years

No usable threat-list result was available for this scan. The score does not establish that the website is free of malware or phishing.
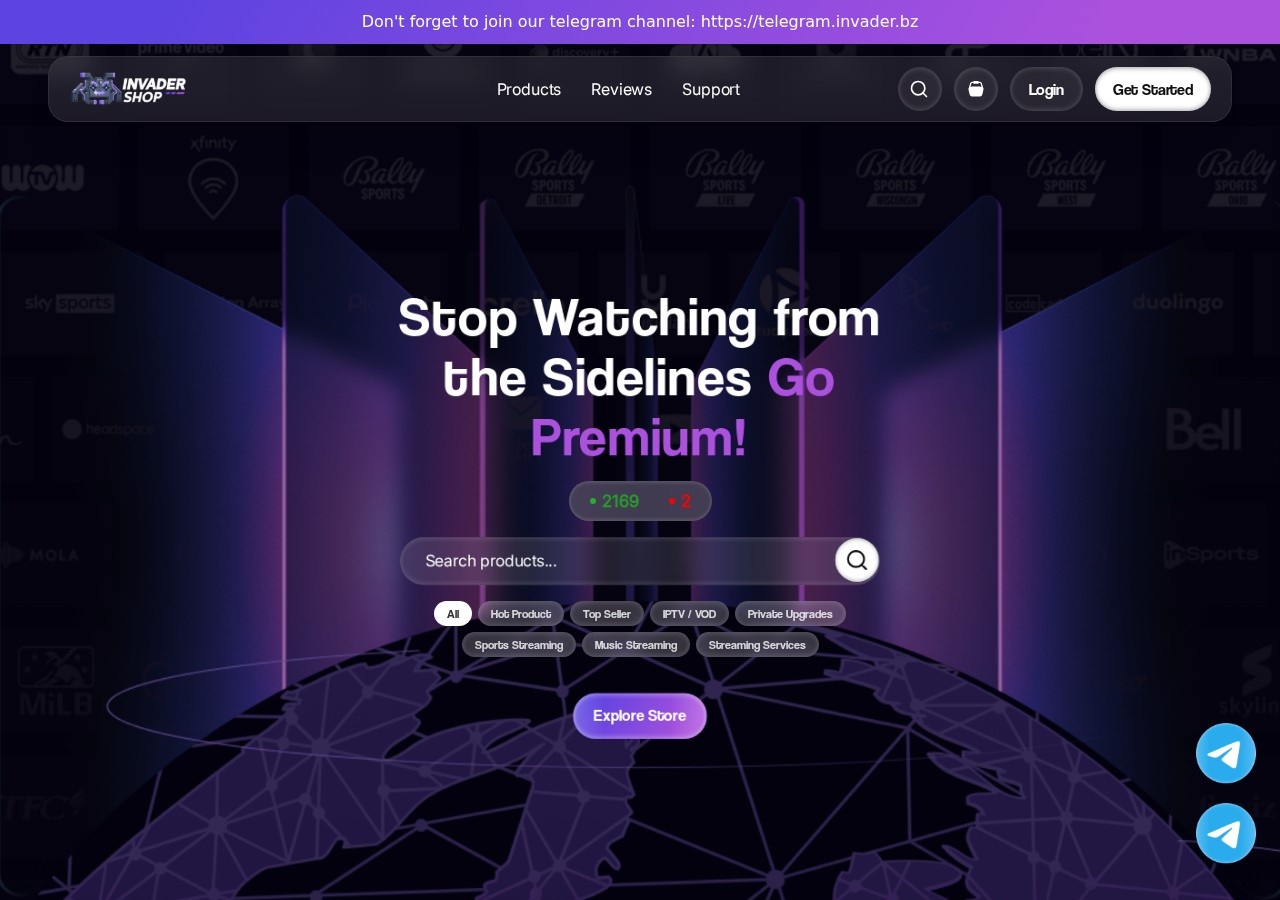
Website Screenshot

Expand view ↗
https://invader.shop/HTTP 200
Remote website screenshot of invader.shop

Static remote image · November 16, 2026. The target website is not embedded in your browser.

ASSESSMENT SUMMARY

What the evidence says

The scan found a broad set of mature technical, behavioural and transparency signals. Its TLS certificate was valid at scan time. Registration records show the domain has existed for more than two years. The accessible homepage exposed a contact route and linked policy or company information. Confidence is high based on 7 distinct evidence groups collected during the latest scan. The result is a risk assessment, not proof that invader.shop is legitimate or fraudulent.

25 positive factors1 caution factorsHigh confidence

Connection & TLS

19 / 20
95%

Domain maturity & DNS

13 / 15
87%

Browser security

15 / 15
100%

Identity & transparency

14 / 15
93%

Page behaviour

17 / 20
85%

External reputation

10 / 15
67%
TECHNICAL AUDIT

Connection, browser & infrastructure

Observed at scan time. Missing protections show areas to investigate; they do not by themselves establish fraud.

HTTP Security Headers

RESPONSE AUDIT
HSTS

Enforces HTTPS for returning visitors.

View observed valuemax-age=31536000; includeSubDomains
Present
Content-Security-Policy

Restricts script and resource sources.

View observed valueobject-src 'none'; base-uri 'self'; frame-ancestors 'self'
Present
X-Frame-Options

Controls whether other pages can frame this site.

View observed valueSAMEORIGIN
Present
X-Content-Type-Options

Helps prevent MIME type sniffing.

View observed valuenosniff
Present
Referrer-Policy

Controls referrer information sent to other sites.

View observed valuestrict-origin-when-cross-origin
Present
Permissions-Policy

Limits access to browser capabilities.

Missing

SSL/TLS & Encryption

X.509 CERTIFICATE
Certificate hostname
invader.shop
Validation
Trusted and valid
Issuer
Protocol
TLSv1.3
Cipher
TLS_AES_256_GCM_SHA384
Valid from
November 8, 2026
Expires
February 6, 2027
Days remaining
81
Final destination
https://invader.shop/
Redirects
0

Certificate details describe the submitted hostname. HTTP observations describe the final destination. Fetch time covers the HTTP request and redirects, rather than a browser performance test.

DNS & Domain History

PUBLIC RECORDS
IP addresses
188.114.96.0, 188.114.97.0, 2a06:98c1:3121::, 2a06:98c1:3120::
Nameservers
ajay.ns.cloudflare.com, pola.ns.cloudflare.com
Mail servers (MX)
mail.invader.shop
SPF
v=spf1 ip4:51.81.14.24 ip4:51.81.14.26 +include:spf.privateemail.com ~all
DMARC
v=DMARC1; p=none; rua=mailto:[email protected]; pct=90; sp=none
CAA
Not observed
Registrar
Porkbun LLC
Registered
April 27, 2022
Registration expiry
April 27, 2027

Page Behavior & Identity

HOMEPAGE ANALYSIS
Page title
Cheap Streaming, IN-VADER TV & VPN Accounts | Invader Shop
Contact routes
a contact or support page, a visible email address
Policy / company links
terms page, legal notice, privacy policy
Forms / password fields
0 / 0
External form destinations
0
Hidden frames
0
Mixed-content references
0
Response cookies
0
Cookie attributes
Secure: 0 · HttpOnly: 0 · SameSite: 0
Security contact file
Not confirmed
THE EVIDENCE BEHIND THE SCORE

Positive signals & concerns

Findings are ordered by their scoring weight. Category limits and risk caps can affect their final contribution.

Positive factors

25 FINDINGS

Valid TLS certificate

The certificate is trusted, matches the hostname and is currently valid.

TLS · transport

HTTPS is active

The final page is delivered through an encrypted HTTPS connection.

Transport · transport

Website responded successfully

The scanned destination returned HTTP 200.

HTTP · transport

Established domain registration

Registration records indicate an age of more than two years.

RDAP · domain

Key policy pages are linked

The homepage links to several policy or company-information pages.

Content · transparency
Show 20 more findings

Domain email controls are published

The domain exposes multiple mail-routing or anti-spoofing controls.

DNS · domain

HSTS is present

The response includes the strict-transport-security header.

Security headers · security

Content Security Policy is present

The response includes the content-security-policy header.

Security headers · security

Contact route found

The page exposes a contact or support page, a visible email address.

Content · transparency

Normal homepage content was accessible

The scanner received a usable HTML homepage rather than an interstitial or access-control page.

Content · behavior

No monitored high-risk wording detected

The accessible homepage did not contain the monitored high-pressure or credential-request phrases.

Content · behavior

Responsive origin server

The initial request completed in about 365 ms.

Performance · transport

Public DNS resolution

The domain resolves to 4 validated public network addresses.

DNS · domain

Nameserver redundancy

At least two authoritative nameservers were found.

DNS · domain

Public routing identity found

RIPEstat mapped the address to AS13335 and prefix 188.114.96.0/24.

RIPEstat · domain

MIME sniffing protection is present

The response includes the x-content-type-options header.

Security headers · security

Referrer policy is present

The response includes the referrer-policy header.

Security headers · security

Clickjacking protection

Framing is restricted through X-Frame-Options or CSP.

Security headers · security

Good MDN Observatory grade

MDN HTTP Observatory assigned grade B+.

MDN HTTP Observatory · security

Descriptive page title

The homepage provides a usable browser title.

Content · transparency

Page description is provided

The homepage includes a descriptive meta summary.

Content · transparency

robots.txt is available

The website publishes a non-empty robots.txt file.

Public files · transparency

Substantive homepage content

The scanned page contains enough readable text to explain its purpose.

Content · transparency

No hidden frames or external form targets

The accessible homepage did not expose hidden iframes or forms posting to another hostname.

Content · behavior

Canonical URL declared

The page declares a canonical destination.

Content · transparency

Caution factors

1 FINDINGS

Missing permissions-policy

The response did not include this browser security header. Missing headers affect hardening, but do not by themselves prove fraud.

Security headers · security
INDEPENDENT SIGNALS

Additional security context

Completed provider results collected for this report. These checks cover different aspects of the website.

Google Public DNS

DNS answered

DNSSEC authentication was not confirmed. This alone is not evidence of fraud.

MDN HTTP Observatory

Grade B+

Independent HTTP security assessment: 80 points.

RIPEstat

AS13335

Network prefix: 188.114.96.0/24.

PRACTICAL NEXT STEPS

What to investigate next

Use the findings to guide your checks before sharing data or changing the website configuration.

01

Review browser security headers

Configure HSTS, a site-specific Content Security Policy and appropriate framing, MIME, referrer and permissions controls. Test changes with your application.

COMMUNITY FEEDBACK

Reviews from DarkOra members

Member experiences with invader.shop. Reviews are moderated and shown separately from the automated safety score.

—/ 50 approved reviews

Share your experience

MEMBER ACCESS

Be the first to share your experience

There are no approved member reviews for this website yet.

ABOUT THIS WEBSITE REPORT

Your questions about
invader.shop

Is invader.shop safe to visit?

The scan found a broad set of mature technical, behavioural and transparency signals. Its TLS certificate was valid at scan time. Registration records show the domain has existed for more than two years. The accessible homepage exposed a contact route and linked policy or company information. Confidence is high based on 7 distinct evidence groups collected during the latest scan. The result is a risk assessment, not proof that invader.shop is legitimate or fraudulent.

What is the DarkOra score for invader.shop?

The latest DarkOra website safety score is 88 out of 100, classified as Strong trust signals. The score reflects observable technical and reputation evidence collected during the latest scan.

How is this website safety score calculated?

DarkOra uses six independently capped areas: connection and TLS, domain maturity and DNS, browser security, identity and transparency, page behavior, and external reputation. No single signal determines the entire score.

When was invader.shop last checked?

The report was last updated on November 16, 2026. Website, DNS and certificate settings can change after this time.

Does a high score prove that invader.shop is legitimate?

No. Automated evidence can reduce uncertainty, but it cannot prove ownership, product quality or honest intent. Verify the organization, payment destination, refund terms and independent reputation before sharing sensitive information.

EXPLORE MORE EVIDENCE

Other website reports